Skip to content
PN Scripts

Developer tools

Gatepost

A command-line health check for your domains: certificates, TLS versions, the HTTPS redirect, security headers, cookies, SPF, DMARC and CAA, in one report with a code for every finding.

  • Go
  • DNS (SPF, DMARC, CAA)
  • TLS
  • HTTP security headers
  • Coming soon

Coming soon

Not published on its store yet, so there is no buy or download link. PN Scripts does not take payment for it here.

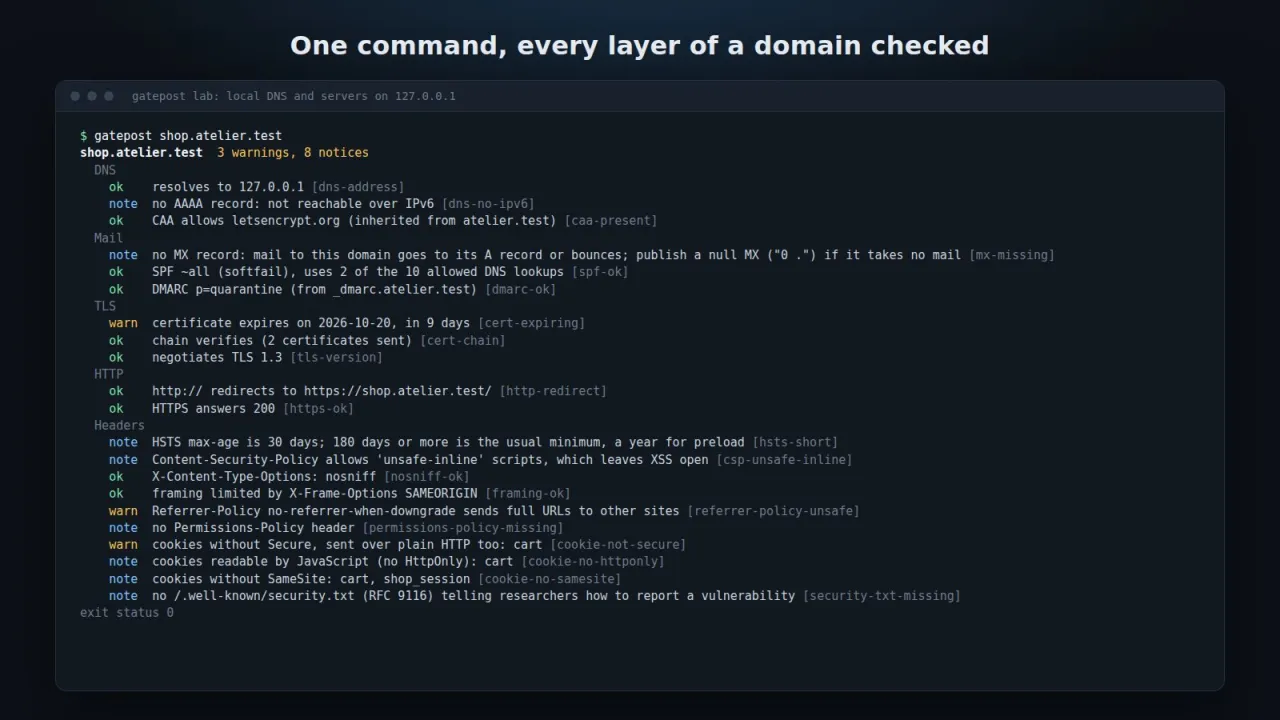
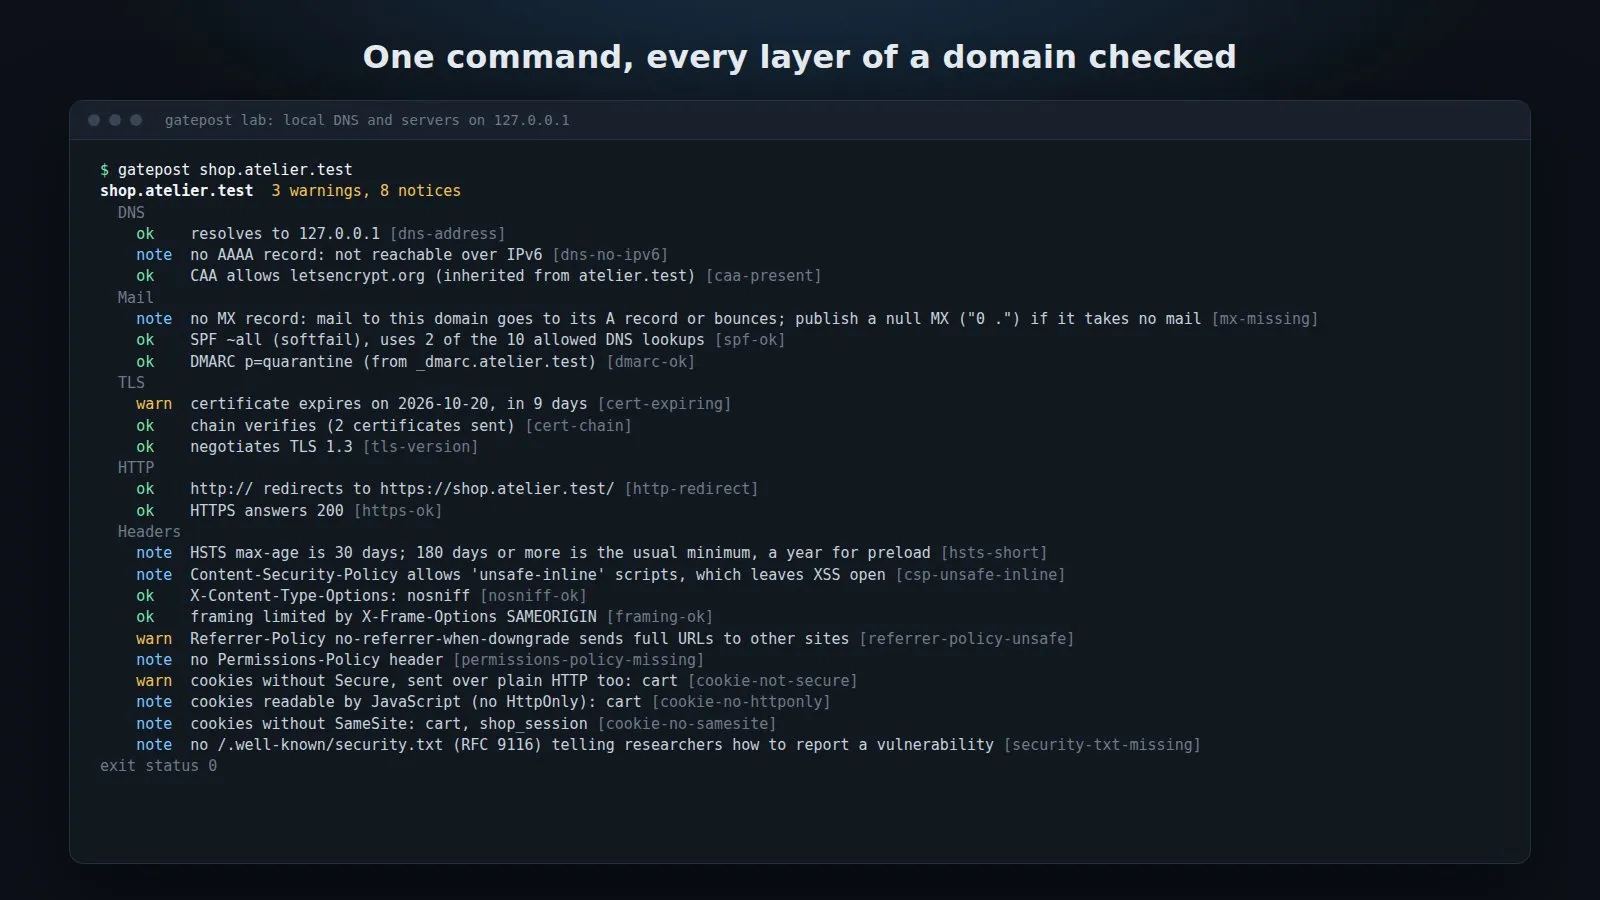
Gatepost terminal report for shop.atelier.test grouped into DNS, Mail, TLS, HTTP and Headers

What it solves

The gap

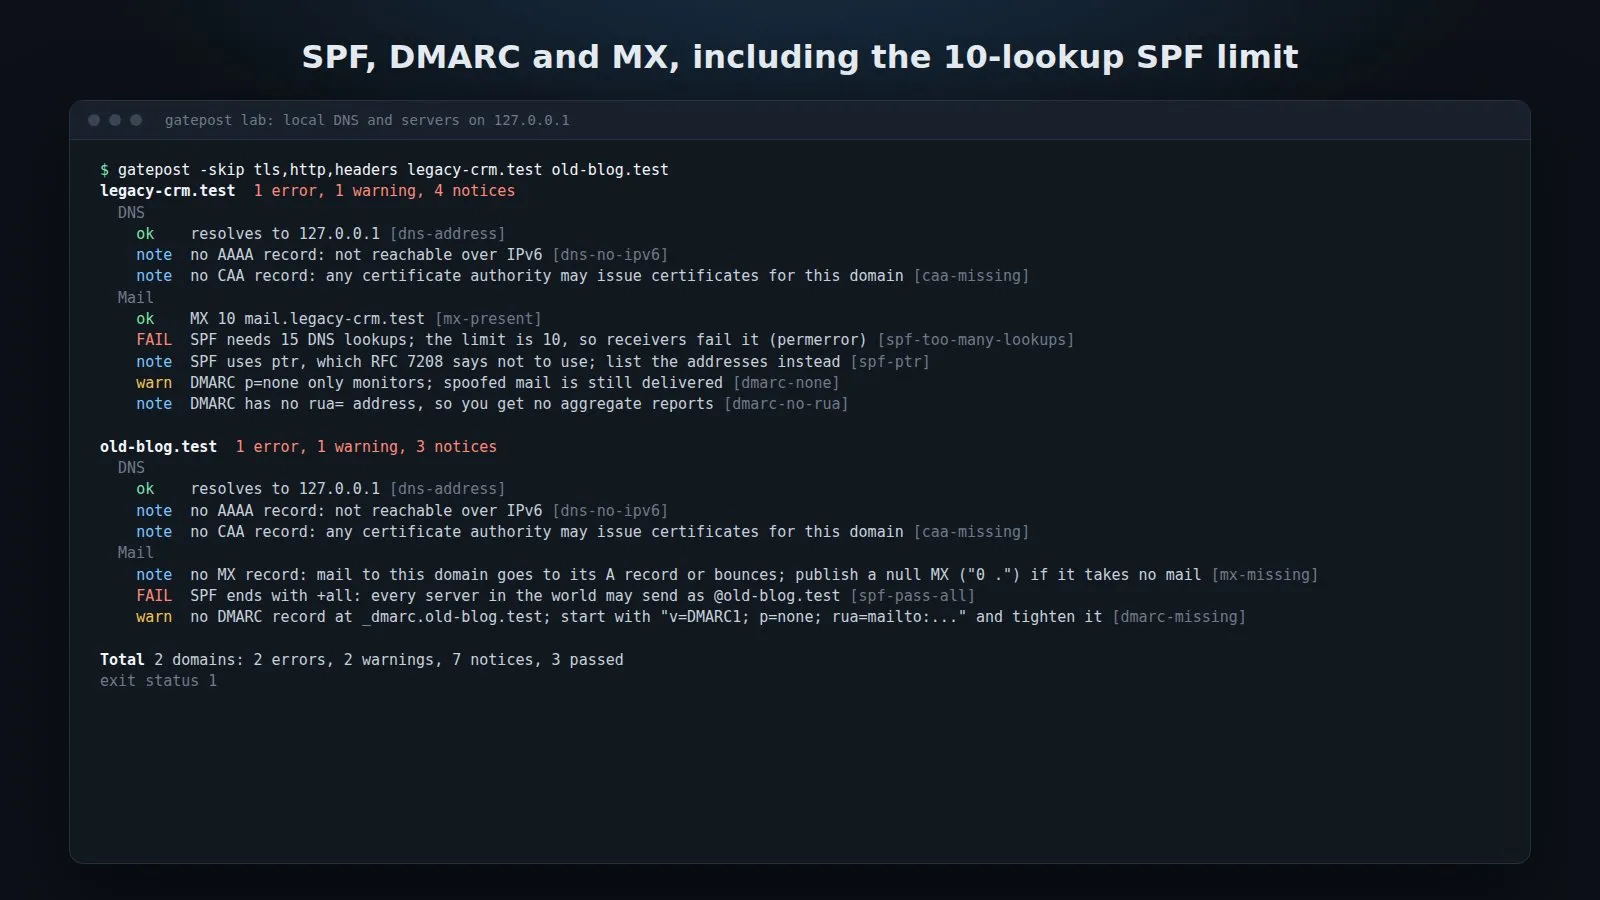
Domains break quietly: a certificate renewal fails on one subdomain, an SPF record passes the 10-lookup limit after a new newsletter tool is added, DMARC stays at p=none for years and an old server still speaks TLS 1.0. Each problem lives in a different tool, so nobody looks until mail bounces or a browser shows a warning.
What it is

Gatepost checks DNS, mail authentication, TLS, the HTTPS redirect and the security headers of every domain in one run and reports each problem with a code, a plain message and an exit code a pipeline can act on.

How you use it

One command per domain, or one file for all of them, replaces a round of web checkers, and the same command keeps watching in CI or cron.

For developers, agencies and administrators who look after several domains, Gatepost is a scriptable, offline-friendly domain check that covers web and mail settings in one report.

Who it is for

Use it when

  • A nightly check of every client domain that mails only when something needs attention
  • Verifying a new server's certificate, redirects and headers before switching DNS
  • Checking SPF and DMARC after adding a newsletter or CRM tool that sends mail

Built for

  • Web developers, agencies and freelancers who look after client domains
  • System administrators and DevOps engineers

What is inside

Web and mail in one report

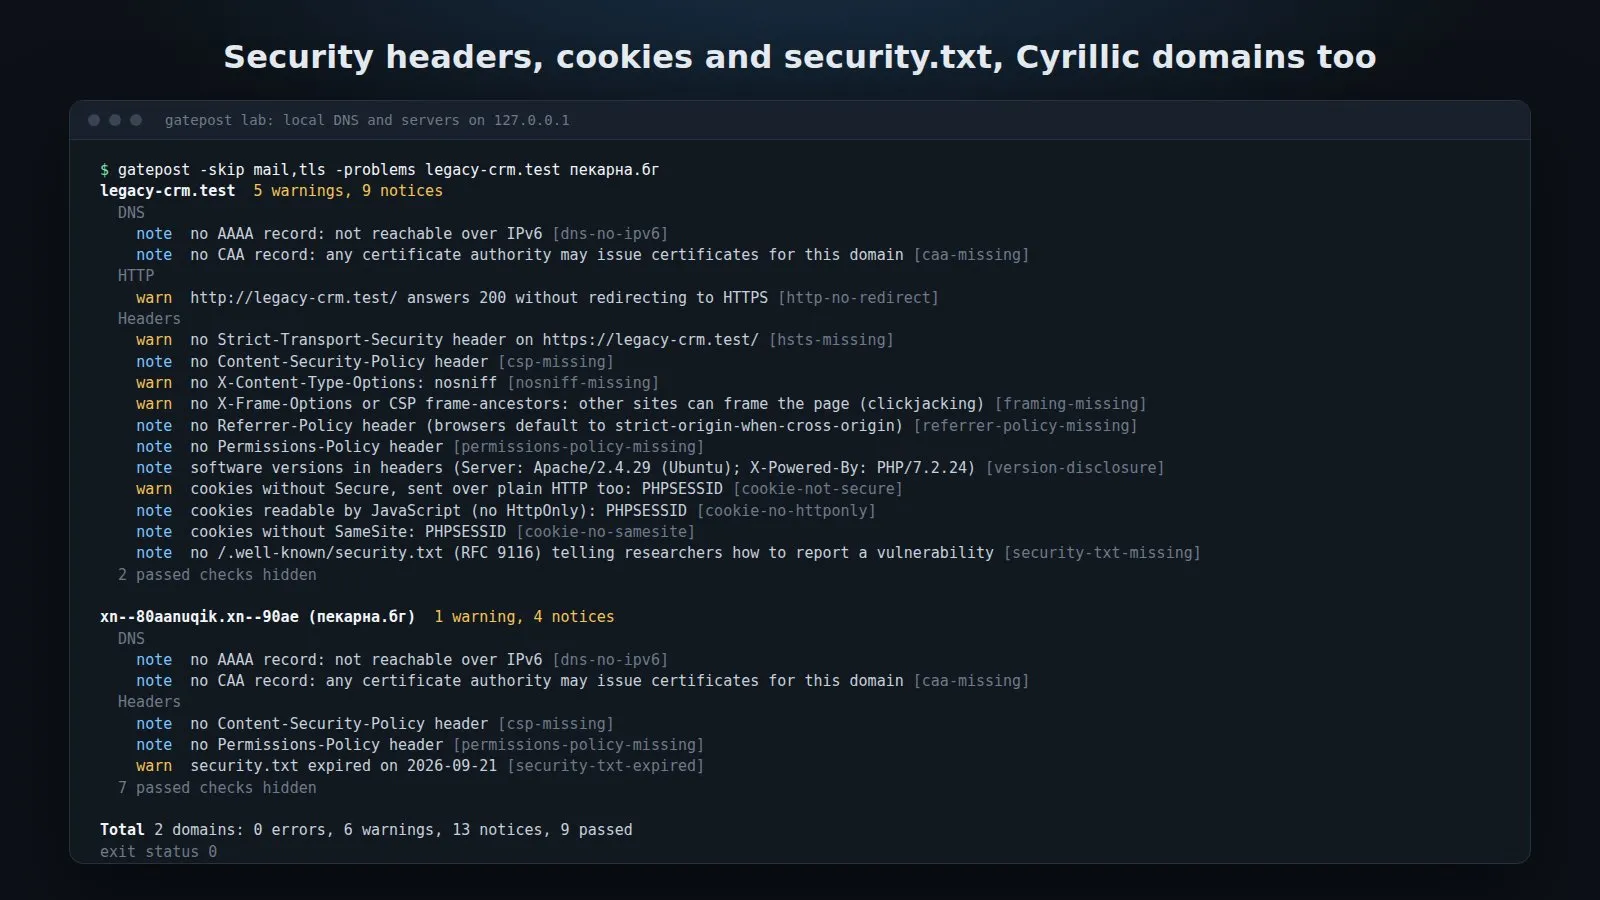
DNS and CAA, MX, SPF and DMARC, the certificate and TLS versions, the HTTPS redirect, headers, cookies and security.txt are checked in one run, grouped by area, with ok, notice, warning or error on every line and a code you can filter or search for.

Problems that other checks miss

SPF lookups are counted through every include and redirect, so a record that passes a syntax check but breaks the 10-lookup limit is caught. HSTS is read on the host itself, not only on the redirect target. CAA and DMARC policies inherited from a parent domain are found and named.

Built for many domains

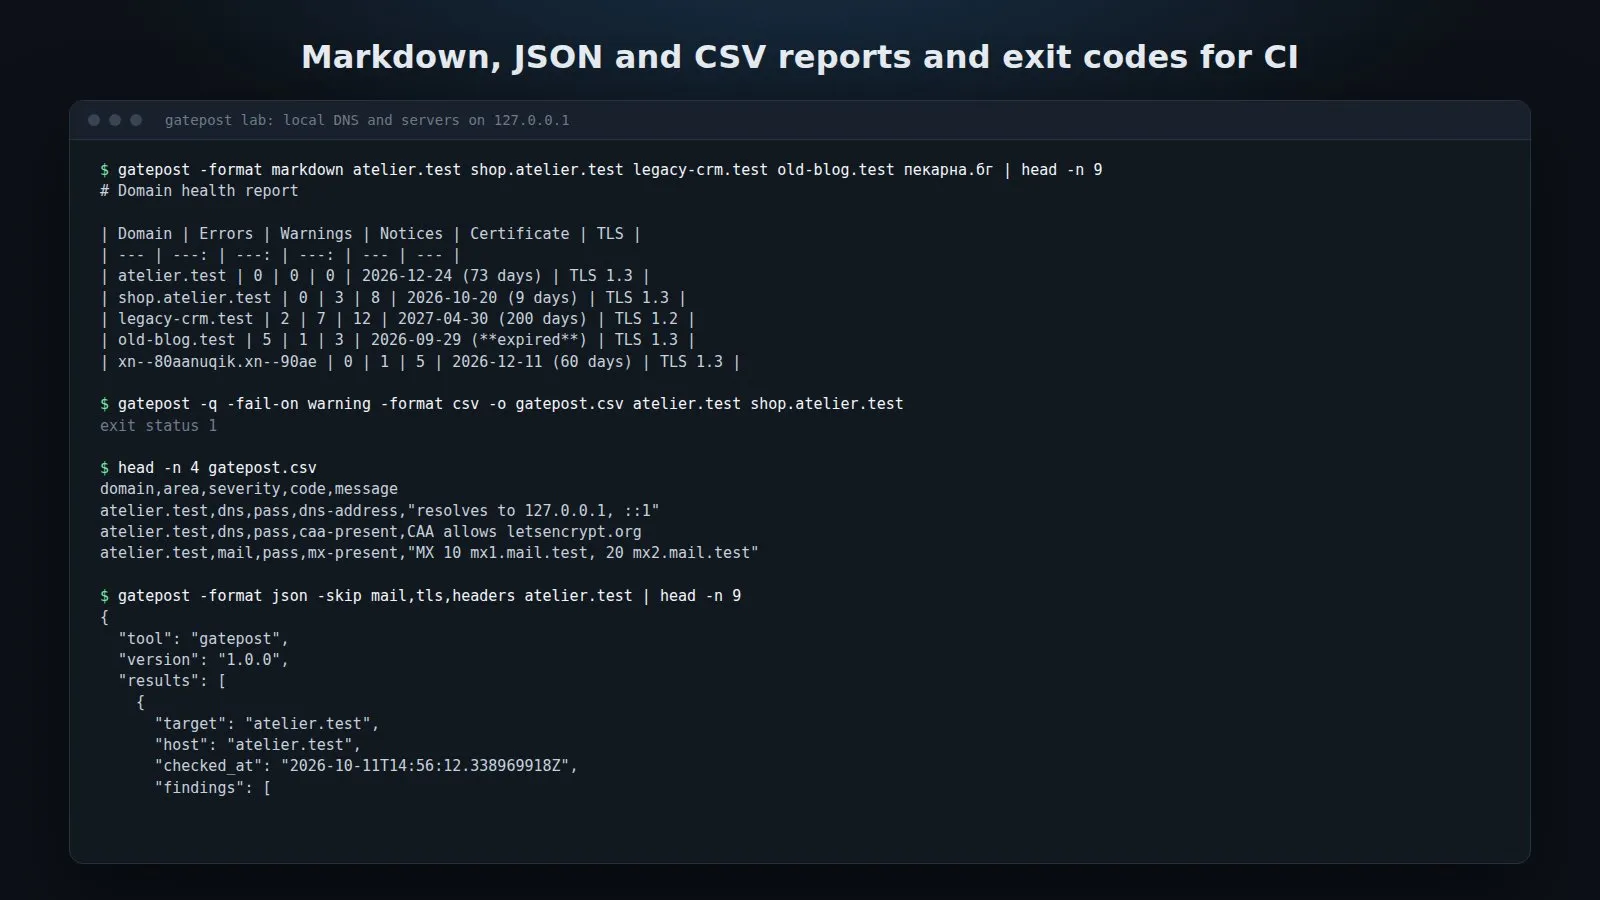
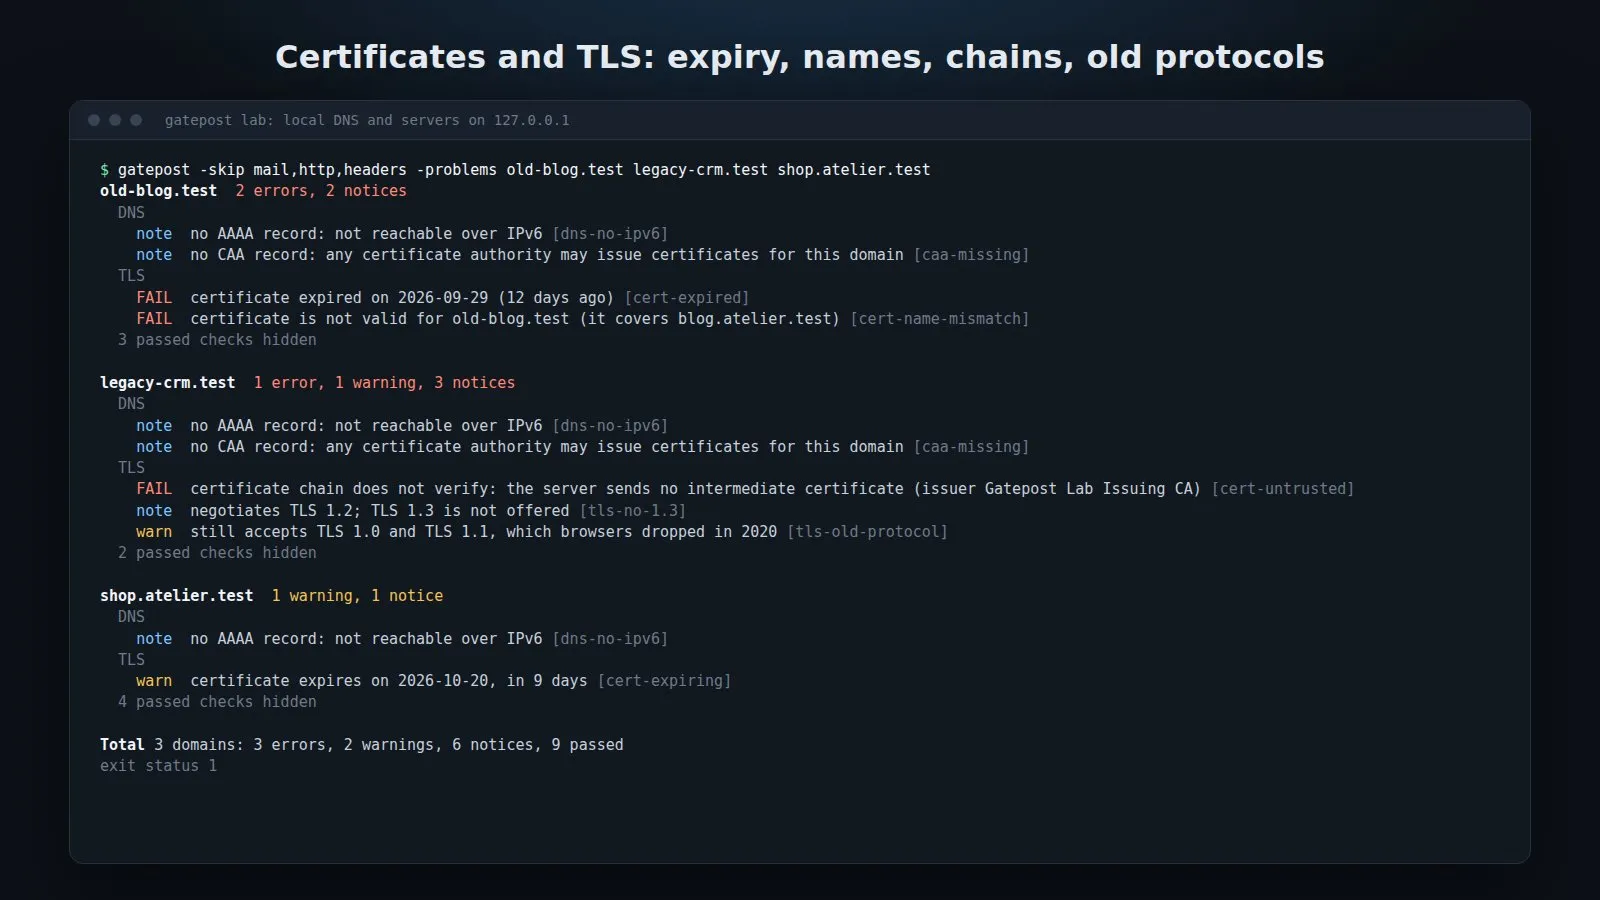
Read domains from a file, check four at a time, hide what passed and get one total line. JSON carries the facts behind each finding, such as days left on the certificate, the SPF record and its lookup count and the redirect hops, for your own dashboards.

Before and after a move

-connect-to points the checks at a new server while the domain still resolves to the old one, -dns asks a chosen resolver, and -ca-file trusts a private CA for internal domains. An offline lab of five domains with typical problems is included for trying everything without a network.

Specs

Availability
Coming soon
Vendor
PN Scripts
Type
App
Platforms
Go
Pricing
One-time purchase Price to be announced.
License
Proprietary
Deployment
Download (prebuilt binaries for Linux, macOS and Windows, plus Go source)
Maturity
v1.0.1

Compatibility

Platform or runtime Supported versions Tested up to
Linux amd64 (binary run) kernel 3.2 or newer Ubuntu 24.04, kernel 6.8
Go (to build from source) 1.22 or newer 1.26.0

Stack

  • Go
  • DNS (SPF, DMARC, CAA)
  • TLS
  • HTTP security headers

Gatepost is coming soon

It is finished and tested. It is not on sale yet; this page will say where to get it when it is.

Coming soon

Not published on its store yet, so there is no buy or download link. PN Scripts does not take payment for it here.

Questions

A command-line tool that checks the outside of a domain: DNS and CAA, MX, SPF and DMARC, the TLS certificate and versions, the HTTPS redirect, security headers, cookies and security.txt, with table, JSON, Markdown and CSV reports and CI exit codes.

Nothing besides the binary for your system: Linux, macOS or Windows on amd64 or arm64. Building from source needs Go 1.22 or newer. Only the Linux amd64 binary was executed during testing.

It checks the front door of each domain and does not crawl pages, scan ports, test for vulnerabilities, validate DNSSEC, check DKIM or test STARTTLS on mail servers. It is not a hosted monitoring service; you run it yourself, for example from cron or CI.

It is written in Go without third-party modules and tested against local DNS, HTTPS and HTTP servers with private certificate authorities, covering expired, misnamed and incomplete certificates, old TLS versions, SPF lookup limits, DMARC inheritance and every header rule. Created with AI assistance; the checks and the CLI were checked by PN Scripts with the automated test suite and by running the Linux binary against the bundled lab and PN Scripts' own domains.

It is not on sale yet. When it is, this page will link to the store; PN Scripts does not take payment on this site.